

The Future of Financial Infrastructure
Is Being Built in the Open
Three days in New York where the technologists who run the world's largest banks, asset managers and market infrastructures work on the problems none of them can solve alone: securing the open source supply chain in a post-Mythos world, governing AI as code, and digitizing regulation so compliance stops being sludge. Not slideware. Production code, open standards and the people who ship them.
Built for the people who build financial technology
OSFF is not a vendor show. It is where financial institutions bring the code and standards they already run in production, compare notes on what broke, and decide together what gets built next. Here is what you take home, by role.
Ship with the projects your peers already run in production
- Hands-on with maintainers of FDC3, CDM, CALM, Common Cloud Controls and Fluxnova, including free Nov 3 workshops (laptops required).
- 70+ practitioner sessions: architecture-as-code, agentic SDLC governance, Kubernetes blueprints, multi-agent orchestration, CDM/DRR developer tooling.
- Major release news on stage: FDC3 3.0 conformance, CALM announcements, Fluxnova 3.0 with MCP support.
See how the industry is patching the open source it all runs on
- OSERA, live: the shared remediation standard, the hardened Spring lines, and how firms pull attested fixes through existing proxies with no CI changes.
- Supply chain keynote with Morgan Stanley, Deutsche Bank and Sonatype, plus Akrites and the upstream response to AI-scale vulnerability discovery.
- Controls as code: Common Cloud Controls, the SDLC Common Controls Catalog, zero-trust AI compute and post-quantum readiness.
Peer exchange at the top, and the numbers to back your strategy
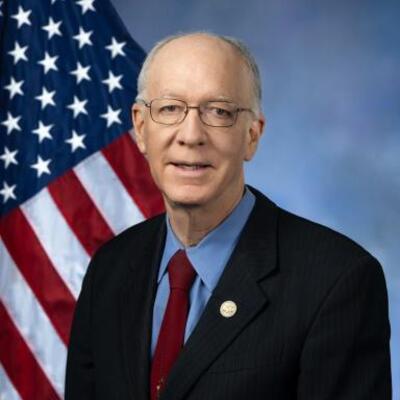
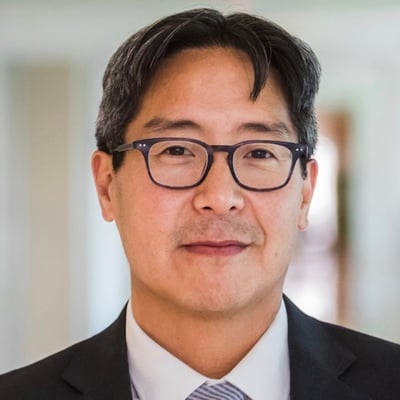
- Policy meets practice: Rep. Bill Foster and former Acting Comptroller of the Currency Michael Hsu on where regulation, AI and open source meet.
- Board-level peers: CIOs, CTOs and MDs from 30+ financial institutions, including the FINOS Governing Board Chair and Vice Chair on stage.
- Fresh industry data: the 2026 State of Open Source in Financial Services launches here, plus membership and project news you will not see anywhere first.
Meet the buyers, and the standards they are buying against
- Two days with the decision makers who set open source, cloud, AI and security policy inside the largest FSIs.
- Build on the stack: become a vendor maintainer under OSERA SLAs, certify against FDC3 3.0, ship tooling on CALM and CCC.
- Be visible where it counts: sponsorship, Fluxnova Con, and a community that now funds its priorities through the FINOS AI Fund and OSERA.
Audience profile based on current OSFF New York 2026 registrations; seniority from self-reported job titles, rounded.
Secure Your Spot at OSFF NY 2026
Registration for Open Source in Finance Week (Nov 3–5) is open, and the venue is capped. One pass covers OSFF and Fluxnova Con on Nov 4–5; the Nov 3 workshops are free but need a separate registration. Member and Non-Member rates available.
Employees of Platinum, Gold, and Silver FINOS member organizations are eligible for complimentary or heavily discounted passes (subject to availability). Check if your firm is a member here. If you work for a member firm and do not have your access code, please email osff@finos.org to obtain it.
Three problems the industry can only solve together
Every keynote, breakout and workshop maps back to one of these. They are the C-level priorities that have turned open source in finance from a cost-saving measure into shared critical infrastructure.
Open Source Supply Chain Security
AI has collapsed vulnerability discovery from weeks to minutes and exploitation now starts the day a CVE is disclosed. The sector runs the same libraries in the same versions, so a flaw in one is a flaw in all. With OSERA downstream and Akrites upstream, the industry is answering with shared standards, shared fixes and shared cost.
- KeynoteSecuring the Software Supply Chain — Dov Katz (Morgan Stanley), Peter Thomas (Deutsche Bank), Brian Fox (Sonatype)
- KeynoteSustaining the Commons: Bridging AI-Paced Security with Upstream Communities — Brent Holden (Red Hat)
- SessionOne Backpatch, Thousands of Repos: Rolling Out OSERA Fixes at Bank Scale
- SessionThe Software Supply Chain Isn't Being Hacked. It's Being Manipulated. — Brian Fox
AI Governance as Code for Financial Services
Agentic AI is already in production across the industry, and governance, not model capability, is what holds it back. FINOS is turning a fragmented landscape of policies and regulations into a machine-readable, runtime-observable pipeline: the AI Governance Framework, CALM, Common Cloud Controls and Fluxnova, funded by the FINOS AI Fund.
- KeynoteGovernance as Code and Fluxnova: Operationalizing Control for Agentic AI — Olivier Poupeney (FINOS), Harish Malavade (Fidelity)
- SessionGovernance, Compiled: Turning the AI Governance Framework into Running Controls
- SessionGoverning the Agentic SDLC with FINOS CALM — Morgan Stanley
- WorkshopArchitecture as Code: CALM Hands-On
Regulatory Sludge & Digitization
Regulation is still shipped as prose and implemented firm by firm, at enormous duplicated cost. Regulation as Code, CDM-based Digital Regulatory Reporting and a machine-readable control catalog make obligations executable, versioned and auditable. On the main stage, a sitting U.S. Congressman and a former Acting Comptroller of the Currency discuss how open source can level up the financial system.
- KeynoteFireside Chat: Leveling Up the Financial System with Open Source Policy — Rep. Bill Foster & Michael Hsu
- WorkshopRegulation as Code: Operationalizing Policy with AI
- SessionRegulation-as-Code: Open, Executable, and Auditable Reporting Pipelines
- SessionCDM/DRR Developer Acceleration: Rune DSL Studio for VS Code — J.P. Morgan
Membership used to be a signal of permission. In 2026 it is a signal of intent.
Banks are funding the AI governance pipeline and OSERA, taking Platinum seats and contributing core infrastructure, because the time from joining to realizing value is now measured in months. The vendor ecosystem has arrived too: technology providers are building on, supporting and certifying against FINOS standards across every mature project. The full numbers, and the names, drop on the main stage.
OSERA: the industry is patching open source together, and it is already in production
In a post-Mythos world, AI-scale vulnerability discovery means the window between disclosure and exploitation has collapsed to a day. Banks run the same open source stacks, so every firm was paying to fix the same CVEs separately. The Open Source Enterprise Resiliency Alliance (OSERA), a FINOS initiative under the Linux Foundation, replaces that fork tax with one shared, member-governed pipeline.
Within 100 days of launch, and backed by Premier members including Deutsche Bank, Goldman Sachs, Morgan Stanley, NatWest and RBC, OSERA published an open Remediation Standard for how a fix must be built, signed and attested before anyone consumes it, and started shipping hardened, FSI-grade releases across the Spring and Java lines the sector still runs: public source on GitHub, member-only built artifacts through the proxies and package coordinates firms already use, with no CI changes.
The first end-to-end release of the OSERA platform lands at OSFF New York. Upstream, the Linux Foundation's Akrites initiative secures the commons; OSERA is the regulated downstream. Come see both on the main stage, and in the hallway where the next projects get prioritized.
Shipped in under a quarter, and what comes next
- Remediation Standard v0.1 published within 3 weeks of operation
- 50+ Spring & Java project lines hardened with attested fixes, available to members in production
- Vendor maintainers under SLA: Moderne delivering patches, ControlPlane building the platform, with HeroDevs, RapidFort, Sonatype and Scott Logic engaged
- 80+ patches per month target, with a per-project sponsorship model so firms can fund what they depend on most
- First end-to-end OSERA platform release unveiled at OSFF New York
- JavaScript ecosystem support expected next
From policy PDFs to running controls: the FINOS Governance-as-Code pipeline
Financial institutions are deploying agentic AI faster than their governance can keep up. The barrier is rarely the model. It is proving to risk, audit and regulators that the agent is compliant, observable and under control. In finance, if you cannot prove it, you cannot use it.
FINOS is filling that last mile with a fully open source, end-to-end Governance-as-Code pipeline: the AI Governance Framework defines what to govern, with risks and mitigations mapped to the EU AI Act, FCA and PRA expectations; CALM turns those policies into machine-readable, validated architecture; Common Cloud Controls and the SDLC Common Controls Catalog supply the controls; Fluxnova orchestrates agents inside governed, auditable processes. Funded by the FINOS AI Fund and built by the institutions that have to pass the audit.
New this fall: The Governance as Code Playbook, a hands-on, CC-BY guide to enforcing AI controls in the build pipeline and at runtime, with audit evidence mapped to the major regulatory frameworks. See it applied live in the Day 1 keynote, then go deeper in the breakouts and the Nov 3 workshops.
Where to see it at OSFF NY
- KeynoteGovernance as Code and Fluxnova: Operationalizing Control for Agentic AI — Fidelity & FINOS
- KeynoteCALM Announcements — James Gough
- SessionGovernance, Compiled: AI Governance Framework → Running Controls
- SessionWho's in Control? Governing AI Agents with FDC3 and Fluxnova
- SessionThe Last Mile of Cloud Controls: Using AI to Operationalize FINOS CCC — RBC
- WorkshopsCALM, CCC, Governed AI with FDC3 Sail, SDLC Controls — Nov 3
Hands-On Technical Workshops
Arrive a day early for free, small-capacity developer workshops led by FINOS maintainers covering CDM Tooling, SDLC Controls, Governed AI (FDC3 Sail), Common Cloud Controls (CCC), Regulation as Code, and CALM Architecture. Pre-registration is required to secure your seat.
Explore All Workshops ↗Fluxnova Con at OSFF NY
Following the transition of Camunda 7 CE, Fluxnova has emerged as a community-governed FINOS project in production at multiple member banks. Join the inaugural summit: three dedicated tracks on BPMN core and architecture, enterprise case studies, and multi-agent orchestration, plus Fluxnova 3.0 with MCP support.
Discover Fluxnova Con ↗The 2026 State of Open Source in Financial Services
Last year's report, produced with Linux Foundation Research, set the baseline. The 2026 edition, with fresh survey data, GitHub activity analysis and interviews with leaders from the largest institutions, is unveiled first at OSFF New York. Be in the room when the numbers drop.
Read the 2025 Report ↗⚙️ Featured Breakout Sessions
A sample of the 70+ sessions across AI Governance, Risk & Security; AI Implementation & Engineering; Platform Engineering; Culture & Business Strategy; and Hot Topics.
One Backpatch, Thousands of Repos: Rolling Out OSERA Fixes at Bank Scale
How a hardened OSERA release actually lands across a bank's estate: proxies, package coordinates, attestations and the operational playbook for consuming fixes at scale without touching CI.
View Session Details ↗Governed Agentic Remediation: CVE Patching and Application Promotion
An architecture that lets AI agents analyze supply chain context, propose CVE patches and request deployment promotion without bypassing strict GitOps controls, aligned with OSERA and FINOS working groups.
View Session Details ↗Governance, Compiled: Turning the AI Governance Framework into Running Controls
From catalog to code: compiling AI Governance Framework mitigations into enforceable controls with audit evidence, including what that looks like for Basel III and Pillar 3 filings.
View Session Details ↗Governing the Agentic SDLC: Driving Agentic Development with FINOS CALM
As autonomous AI agents integrate directly into the software development lifecycle, how a top-tier bank builds the governance frameworks required to keep AI coding safe and compliant.
View Session Details ↗Regulation-as-Code: Open, Executable, and Auditable Reporting Pipelines
Turning approved regulatory obligations into executable, versioned, testable and auditable reporting pipelines, the practical end of removing regulatory sludge.
View Session Details ↗CDM/DRR Developer Acceleration: Early Preview of the Next Rune DSL Studio VS Code Extension
An early look at how institutional developers are accelerating regulatory reporting and data modeling with high-performance Domain Specific Language tooling in VS Code.
View Session Details ↗An Open Source Blueprint for Financial-Grade Kubernetes: Morgan Stanley, Microsoft, and FINOS CCC
A reference blueprint for running Kubernetes to financial-services control standards, built jointly by a bank, a hyperscaler and the Common Cloud Controls community.
View Session Details ↗The Border Is Porous: What Open Source and InnerSource Can Learn from Each Other
A panel of global bank leaders on when to contribute upstream, maintain an internal extension, or fork, and the cultural bridges between internal standards and external ecosystems.
View Session Details ↗There is no CVE for Burnout
The human element of supply chain sustainability: developer health, maintainer burnout, and how enterprises can better support the communities whose code they depend on.
View Session Details ↗
The future of financial infrastructure is being built in the open.
Whether you are committing code to critical infrastructure, securing the software supply chain, governing agentic AI, or turning regulation into something a machine can run, OSFF New York is where the industry aligns. Be in the room.
Easter Egg: Reading closely? Use code 26YTOSFFNY20B for 20% off standard registration. Limited time.